All Top Banking

Showing posts with label Triple DES. Show all posts

3DES, DUKPT & E2EE Explained

Posted by John B. Frank Thursday, May 14, 2009 0 comments


I received a couple questions via email and wanted to take the time to provide a "coupla" of answers.  If you have any questions about anything I've blogged about over the past year, feel free to shoot me one. I've got my email below:

Here's the first question:

Q:  Is Triple DES a better encryption standard than DUKPT?  (Derived Unique Key Per Transaction)?

A:I've used the terms Triple DES and DUKPT quite a bit in recent posts. To clarify, let's just start by saying that DUKPT does not reallycompete with Triple DES.  Let's go over them one by one.

The DES stands for Data Encryption Standard, a block cipher that wasselected as an official Federal Information Processing Standard (FIPS)for the United States in 1976.

Triple DES, sometimes shortenedfurther as 3DES, increases the difficulty of cracking the encryption byapplying three rounds of action: an encryption, a decryption and anencryption, each with independent keys.

3DES has becomepopular for encrypting financial transactions because it is potentiallyfar more secure than DES, which has been shown to yield its secretssomewhat quickly to relatively cheap hardware.

Both DES and 3DESuse a symmetric key. In other words, the same key enciphers anddeciphers the protected data.  To keep the key secret, a secure key-management system is required.

Worldwide, POS devices handle billions oftransactions per day.  If the keys to even a small portion of that traffic was discovered, we'd have a tremendously huge problem.  Which is my segway to DUKPT.

One way to prevent fraud is to use a different key for "eachtransaction," (Derived Unique Key PerTransaction)   HomeATM's secure devices (and thus your transactions) are "Protected by DUKPT" and each one is initialized with amaster key.   The master key is from which the unique keys are derived, one for each"per" transaction.

The benefit of DUKPT is that even if an attacker discovered the key toa particular transaction, none of the other transactions from the samedevice would be able to be decrypted with that key.

That  said, a potential attack point (from a fraudster) would be themaster key stored in the encrypting device. However, because HomeATMuses DUKPT, our device is built so that tampering with the device wipesthis master key out.

These derived keys are used to encrypt transactiondata with a symmetric cipher such as 3DES. HomeATM also takes it onestep further and encrypts the Track 2 data as well.  If you ever haveany questions regarding financial transaction security or how HomeATMprovides true end-to-end-encrypted transactions, feel free to email me. 

Before I get to the next question, I've got one for you. 

When you "type" your card number into a "box" on a merchant website, is it protected by DUKPT?  Is it encrypted?  If so, DES or 3DES?  First one to send me the correct answer gets a Free HomeATM PED!

Q: What is TRUE end-to-end encryption?  (E2EE)


A: First of all, "true"end-to-end encryption can only occur with a PIN based transaction.  Itdoesn't exist outside of that scope because there is a point in theprocess where the cardholder data is decrypted and before it is re-encrypted is that is the point where it is vulnerable. 

With that said, Heartland's proposal for end-to-end encryption has promulgated E2EE into a hot topic.

I would point out that Heartland's E2EEproposal came "AFTER" their breach...while HomeATM institutedtheir end-to-end encryption from "the very beginning."  I'm not bragging.  I'm proudly displaying our insight into the weaknesses inherent in the payments system and  how we improved upon said weaknesses.

But let's get back to Heartland, shall we?  In this post I will attempt to explain why they CANNOT magically snap their fingers and introduce E2EE on their own.  They need cooperation from others in the industry.

Whileit's true that some large U.S. retailers encrypt cardholder data while in transit,  it's also true that most don't.  Therefore...in order for E2EE to work, a lot of retailers would need to revamp their system(s).  Very costly indeed.

Inaddition, the top full-service U.S. payment processors also don'tcurrently support E2EE;  thus, retailers that encrypt card datain transit typically must decrypt it before they send it to theirprocessor. 

The key word here is decrypt.  That is the weak point, the vulnerability,  and as such, also the problem. 

That said, PIN Debit is an entirely different animal.  Card brand standardsrequire that PINs are encrypted end-to-end.   In fact, speaking about Heartland's quest for E2EE, Distinguished Gartner Analyst Avivah Litan stated: 
End-to-endencryption would be most effective if data was encrypted from the timea card was swiped at a POS until it reached the card issuer, similar tothe way personal identification numbers (PINs) currently are encryptedaccording to card brand standards.
Starting to get the point?  If not here's some more insight as Ms. Litan went on to state:
"Heartland is limited by the scope of systems it manages and from which it accepts data;it can only seek to influence the card industry to carry end-to-endencryption beyond the processor stage, through the card networks andonto the card issuers.

"The proposal's success also depends on merchants' willingness to invest in terminal upgrades that support card data encryption."

(Editor's Note: For instance...HomeATM's PCI 2.0 Certified SafeTPIN PED which also encrypts the Track 2 data.)  Avivah continues:

"If Heartland implements its proposed project more securely than it hasmanaged in the past with its network, it will make payment cardprocessing more secure for merchants, especially if they don't managethe encryption keys and leave key management to their processor. 
 
Nevertheless, the process will always include vulnerabilities at the point where data is encrypted and decrypted. 

"Thesevulnerabilities can be limited by using "sound key managementpractices" and enforcing extra security measures, such as "requiringtwo separately managed sets of keys for cryptographic operation" 
Can you provide an example of a "sound key management practice?  That's why HomeATM is the closest thing to TRUE end-to-end encryption in the industry.  (our industry being eCommerce payments and Real Time Money Transfer.) 

In the bricks and mortar world, end-to-end encryption doesn't exist and the whole system would need to be revamped.  You can learn more about that in this related post where Avivah Litan asks:


Reblog this post [with Zemanta]

Nostra(para)digmus

Posted by John B. Frank Thursday, March 5, 2009 0 comments


I
've posted quite a few times that we're in the midst of a major Paradigm Shift. (use the HomeATM search bar on the right and "enter paradigm shift" to read) I took a moment to outline (see graphic on left) some of the finer points which provide e-vidence of this impending shift.

I am positive that convenience will be forced to take a backseat to security which is clearly going to be in the drivers seat.

Likewise, I am more confident that in order to secure a transaction it has to be done by Hardware. No predictions there...just fact. To the engineers at HomeATM...it's a foregone conclusion. It doesn't matter what anyone says today... tomorrow always shows us the truth.

Truth is, hardware is not a "better" option, it's the only option. Software is breached 92% of the time vs. only 1% for hardware.

One doesn't need to be Einstein to figure out that if something is breached 92 times more than something else, then the "something else" MUST be more secure.

Question: If something is breached 1% of the time vs. 92%, then wouldn't it be at least 92 times easier to to "fix" what causes 1% of breaches?  In the case of hardware being breached, tampering was virtually to blame everytime. So we made our SwipePIN device tamper proof. We're done.


When you consider new cracks in Secure Socket Layer(SSL) websites , DNS hijacking, Man-in-the Middle Attacks (MITM) Malware, bots, and combine that with the fact that there's been3 Major Processor Hacks in 3 Months, these are indeed dangerous times. This doesn't even take into account the YTBD hacks which will occur in the near future.


We're all at risk for loss if we believe that a PIN Based solution can be peripheraless. Once again, Hardware is not an option. IBM came to the same conclusion whilst looking at how to best secure online banking. See: IBM Agrees with HomeATM....Hardware Required.

Information security will become the number one priority for EVERYONE, and the ONLY way to securely transact an e-commerce transaction is via hardware. There is NO other way. Besides...what's the anti-convenience rhetoric about Hardware anyway?  Doesn't it make it more convenient when you don't have to type in a bunch of digits, expiration dates or CVV's. 

Besides...we're used to hardware...don't you have to plug a cigarette adapter into your iPhone or Blackberry to charge it? How hard is that?  Well, in addition to processing PIN Debit, you can plug in the HomeATM SwipePIN device and "charge it."  What's the difference?  Plug in cell-phone to charge it...Plug in SwipePIN device to charge it. 
(Don't forget about our PIN my Card application which allows you to securely assign a PIN number to your credit card, providing a more secure dually-authenticated transaction) 


The Internet is demonstrating significant power to provide "Net"profit", Cash has been replaced as King, having being "overthrone" by King Debit, and information security is more important than ever. It doesn't take Nostradamus to write a quatrain predicting that EFT Networks will want their piece of the PIN Debit/Credit Internet Pie.  And rightly so!  Why should they be "shut out" from Internet transactions?  

PIN Debit leads Signature Debit 45%-35% in the physical world, but doesn't yet exist in the virtual one. Can you possibly disagree that the paradigm shift will contribute towards bringing PIN Debit to the web? Problem is...in the past retailers were the focal point of hackers. Got the Personal Account Numbers but never the PIN. Now it's processors. 100 Million Personal Account Numbers...Zero PIN's.

PIN's are the Holy Grail to Hackers. Doesn't ANYONE SEE (beside's Avivah Litan, HomeATM and IBM) what's going to happen if we attempt to secure them in a software environment?

Nostra(para)digmus predicts that no matter what we see today, tomorrow will show us the truth.


Reblog this post [with Zemanta]

PIN Debit and PCI Compliance

Posted by John B. Frank Tuesday, January 13, 2009 1 comments

Howard Riell, in an article written for Convenience Store Decisions, writes about PCI compliance.  As you'll undoubtedly notice while reading the article, PIN entry devices, or PED's are an integral part of PCI certification. The long and the short of it is that all PED's must be certified by PCI-approved laboratories and encrypt PIN's with Triple DES.  I know how that's done with a hardware device...(we're in the midst of getting our personal swiping device tested and approved for PCI compliance) but I'm not quite sure how it would/could/should be done with a software application.  (See "Software Breach 92 Times More Likely Than Hardware")

Here's some snippets from from the CSN story, entitled: "The High Stakes Of Compliance:"

It was in September 2006 that the credit card companies formed the PCI Security Standards Council in the hopes of battling fraud. Today, all merchants who accept payment card transactions must comply with the PCI Data Security Standard or face sizable penalties.  Indeed, the passing grade for PCI is 100%, which means failing even one of the criteria will bring consequences...

Editor's Note:  So, it's obvious that these Triple DES mandates are an integral element of PCI compliance and in 5+ months TDES is required on "all debit transactions." Since Jan. 1, 2008, all newly manufactured debit card processing terminals must incorporate PIN entry devices that have been certified by PCI approved laboratories

  • By January 2009, newly installed fuel pumps that accept debit cards must feature PCI-compliant encrypted PIN pads.  See "Triple DES for GAS" 
  • Manufacturers have to begin installing key pads capable of implementing a new Triple Data Encryption Standard (TDES), which requires that data be encoded several times through an encrypted PIN pad.
  • By July 1, 2009, TDES will be required for all debit transactions and by
  • June 30, 2010, all fuel dispensers will need to be able to encrypt PINs according to the TDES.
The very next day, July 1st 2010, pumps that process debit transactions must be upgraded with encrypted PIN pads, and in-store POS terminals have to be certified as PCI-compliant.  The devices must also process all debit transactions using TDES.

One of my favorite lines from the article comes from Bruce Snyder,
manager of IP retail systems for 395-store Kwik Trip based in La Crosse, Wis“ who instead, sounds like a spokesman for Gemalto.  (see: Gemalto Wants EMV in US)  Apparently he doesn't like the implementation costs (retailers will need to replace outdated hardware) and thinks that as long as they have to get new equipment anyway, then V/MC and the banks should spend billions to implement EMV and when they're done, he'll replace Kwik Trip 'sexisting equipment with Chip and PIN readers.  Problem is, it won't be Kwik...it'll be years, if they started today.  (don't hold your breath)


"We have this silly little mag stripe that is so vulnerable and penetrable and we are building an infrastructure around it to protect the information, and a lot of people are making good money on that,” Snyder said. “With the new rulings on EPPs, if I want to continue to do debit we have to replace all of our dispenser doors and PIN pads at a huge expense to us to remain compliant. What we have to do is put in an encrypted PIN pad at the dispenser if we want to continue to do debit there.” But the new door and PIN pad will cost $1,500 per dispenser. (Ouch!  Consumers can get our SwipePIN device for merely the cost of shipping and handling, which in the face of $1500...makes for a rather compelling value proposition)

“Start doing the math on that and now you have to make a decision: can we afford to do this? And what happens if we don’t?” Snyder said. “We need to change that method of presenting ourselves for a credit transaction and make it more secure so that we don’t have to build all of this stuff around it to try to protect a very flawed method...”


Read the complete story at Convenience Store Decisions


Reblog this post [with Zemanta]

Powered by Blogger.

Search This Blog

Our Manufacturing Facility

Learn More About Us

Find out how our patented technology can empower your financial institution.

Our secure two-factor online banking authentication eliminates dangerous passwords and usernames and replicates the same trusted process used to access cash at ATM's. (Insert Bank Issued Card, Enter Bank Issued PIN)

There is an R.O.I. as FI's also earn recurring revenue from each transaction conducted using our PCI 2.0 Certified PIN Entry Device. Our technology also provides a unique real-time P2P "Instant-Transfer" which allows your online banking customer to transfer cash from ANY of their bankcards to ANY other bankcard...with the Swipe of a card.

Help your bank eliminate phishing and your customers avoid identity theft by providing them with the ability to stop typing and start swiping. There is no safer way to conduct financial transactions online than by 3DES DUKPT encrypting the cardholder details, which we do at the mag-head "inside the box/outside the browser."

Total Pageviews

SLIM for PC or SmartPhone

SLIM for PC or SmartPhone
Click to Inquire

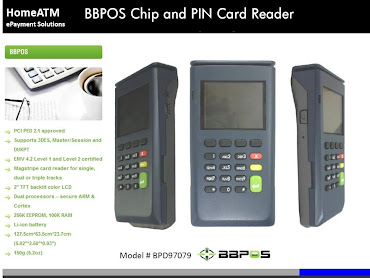
Chip and PIN eCommerce and Mobile

Chip and PIN eCommerce and Mobile
Click to Inquire

Kapersky Calls for Mass Adoption of Card Readers

Kapersky Calls for Mass Adoption of Card Readers

Translate This Blog

BobCaps

Search ePayment News (example: NFC)

About Me

My photo
Named one of the best Payment Industry News Blogs 4 Years Running

Feedjit

My Zimbio